Cyber Espionage is a cyberattack carried out to gather intelligence — usually by a nation-state or state-linked group — rather than to make money directly. That is the core difference from typical cybercrime: a financially motivated attacker wants a payout, fast, through ransom or stolen data they can sell.
An espionage actor wants access, quietly, for as long as possible, and usually is not trying to get paid at all.
A financially motivated attack tends to be loud and fast: a ransom note, a locked system, an extortion demand with a deadline.
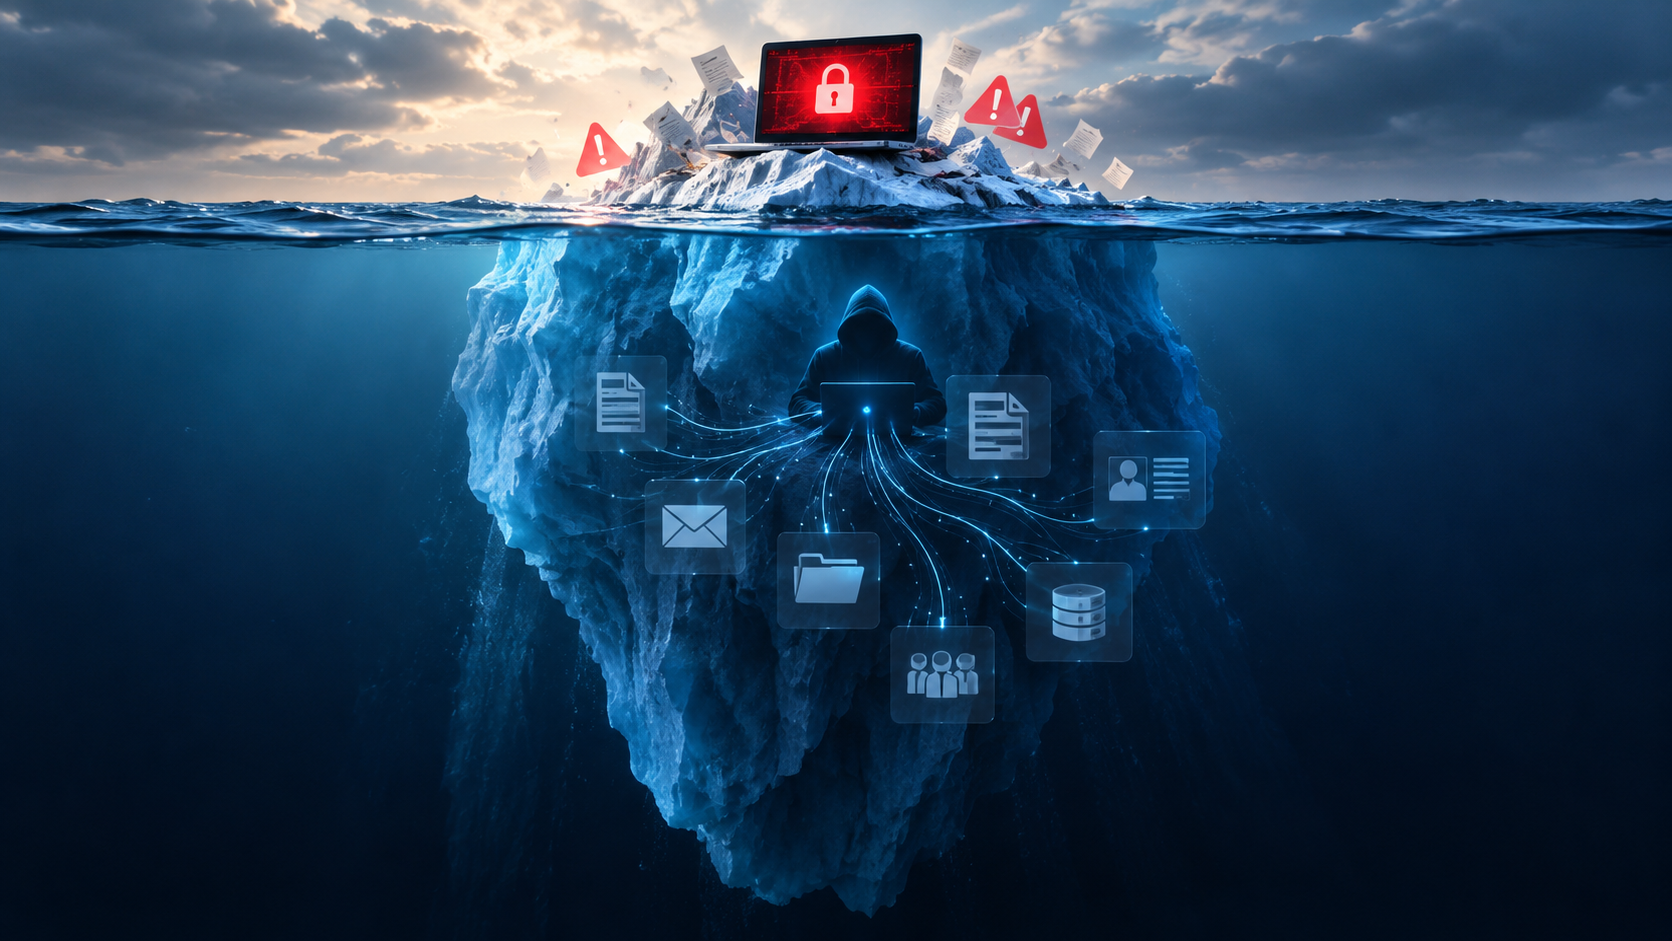
A cyber espionage operation tends to be the opposite. An attacker who gets in, stays hidden, and collects information over months or years without you ever knowing they were there.
Espionage actors are playing a longer, quieter game.
Even though most agencies will face the financially motivated kind, knowing the difference changes how you think about response.
A ransomware attack demands an immediate, visible reaction.
A quiet, long-term intrusion requires you to actually look for what isn’t obvious.
Understanding both threat types means you are not caught assuming every incident looks like the ransom note. It also changes what you put in place ahead of time.
Someone should be watching your access and your activity every day. If something does slip through — next week or a year from now — the response should already be arranged.
With our cybersecurity in place, the support and zero-cost remediation are already included, so you’re not negotiating scope and price in the middle of an incident.